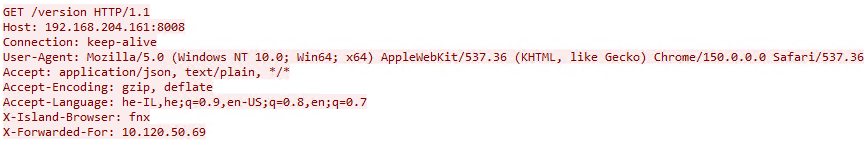
Island sends a GET request to /version endpoint (probably how they health-check the Core):
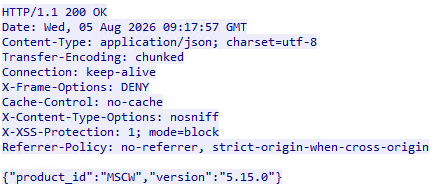
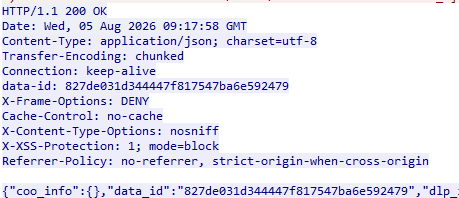
Core responds:
Island sends a GET /hash request with the downloaded file’s MD5 hash:
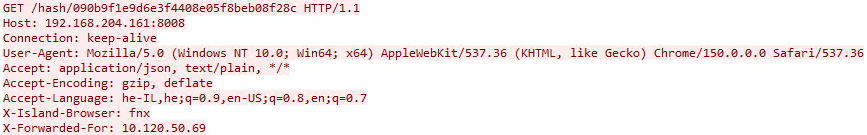
- No “rule” header - the scan result fetch is checked against all Core workflows
- No “timerange” header
- Given that both headers don't exist in the GET /hash request, Island basically asks for a scan result independent of a workflow or time range - if a scan result exists for that file in the processing history in Core, it will be returned, even if AVs have been updated since then, or workflow changes have been applied, etc...
After the GET /hash request, OPSWAT might return one of the following two options:
Option A - OPSWAT Returns an existing scan result
2 severe issues:
- The GET /hash request fetches the first existing scan result of the file regardless of the rule it was scanned with and timerange (today might’ve been allowed but tomorrow all AVs might detect the same file as Infected but Island will keep fetching the old scan result, according to Core's processing history retention).
- OPSWAT Admins also might be confused in the following scenario:
File ‘X’ is blocked due to being blocklisted by Metadefender Core -> Admin excludes the file from blocklist in the workflow (policy) in Core -> Admin requests user to download again -> Client still sees file as blocklisted, OPSWAT Admin doesn’t see an additional POST request coming from Island or a new scan entry in processing history in Core.
Option B - Core returns scan result "Not Found"
If Core returns “Not Found” for the GET /hash request then Island proceeds to send a POST /file/sync request:
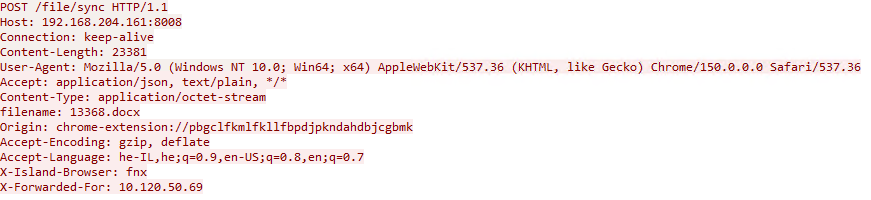
Core scans the file and returns the result:
UPDATE 09/11/2026 - WORKAROUND
Island have not resolved the issue as of yet (adding a time-range header or disabling their /hash/<MD5> GET request from being sent to Core entirely.
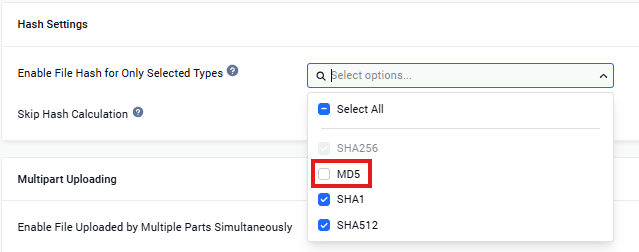
A workaround I raised internally is disabling MD5 Calculation in the Core workflow (possibly all workflows). As a result every scan request will be kept in processing history with no MD5 hash record, resulting in Island’s GET /hash/<MD5> request to return “Not found” and send the file to be scanned on every download request.
Disabling MD5 hash calculation will have to be done at minimum on the workflow the Island uses, but preferably on all workflows.
The setting is inside the workflow, under "General->Hash Settings".
Was this article helpful?
That’s Great!
Thank you for your feedback
Sorry! We couldn't be helpful
Thank you for your feedback
Feedback sent
We appreciate your effort and will try to fix the article